
Rescue: security hardening
Make your site a harder target.
Old plugins, shared logins and missing backups are the usual ways in. We find your site’s risks, rank them and close them, then tell you in writing what’s left.
You get it in writing. A ranked list of risks, what we changed, and what risk remains.
Check first
Signs your site needs hardening
Had a flood of failed logins, or a plugin warning from your host? Or just know the site’s been left alone? Check these six.
Plugins not updated in months. Old code is a common way in.
Shared admin logins. Several people, one account, no record of who did what.
No two-step sign-in. One guessed or stolen password is all it takes.
No off-site backups. If your host loses the site, the backup goes too.
A control panel nobody checks. Old users and host warnings pile up unseen.
Ex-staff or old developers with access. Logins outlive the people who needed them.
Right now
While you wait for us
Go steady. A few safe steps help now, and a few rushed ones make things worse.
Safe to do now
- Change the main admin password from a device you trust. Make it new, not reused.
- Remove ex-staff accounts you’re sure about. Leave any doubtful ones for the review.
- Keep your host’s warning emails. They tell us where to look first.
Please don’t
- Install “security” plugins in a panic. They clash, slow the site and can lock you out.
- Delete files or plugins you’re unsure about. The site may still need them.
- Send passwords by email or chat. We’ll send you a secure link instead.
Service options
Choose the scope of work
The review tells you what’s wrong and changes nothing. Hardening fixes it. Monitoring keeps it fixed.
01
Security review
A written, ranked list of your site’s risks. We look, but we make no changes.
- Every admin, host and developer login listed
- Plugin, theme and core versions checked
- Hosting control panel and backups checked
- Sign-in and file settings checked
- Written risk list, most urgent first, in plain words
- Not included: making any of the changes
- Not included: setting up backups or monitoring
02
Recommended
Hardening
We make the changes on the list, test the site, and write down what risk remains.
- Everything in Security review, plus:
- Old accounts removed, passwords reset
- Updates applied, unused plugins and themes removed
- Two-step sign-in for every admin
- File and login protection
- Off-site backups, with a test restore
- Written report of changes and remaining risk
- Not included: monitoring after handover
03
Hardening and monitoring
The full hardening, then we keep watching the site and keep it patched.
Choose hardening and monitoring
- Everything in Hardening, plus:
- Uptime and malware monitoring
- Updates applied and tested before they go live
- Alerts on new admin users and changed files
- Off-site backups kept, with regular restore tests
- Monthly written log of checks and changes
We assess the problem and confirm the scope and next steps in writing before work starts.
How it works
How hardening works
Six steps, in this order. We tell you before any change to how you or your staff sign in.
Security review only? We check each step and send the ranked list from step 06, without changing anything.
01
We review access and accounts.
Every admin, hosting, email and developer login is listed. We agree with you which ones go.
02
We update, and remove unused code.
Core, theme and plugins are updated and tested. Plugins you don’t use come out, because switched-off code can still be attacked.
03
We turn on two-step sign-in.
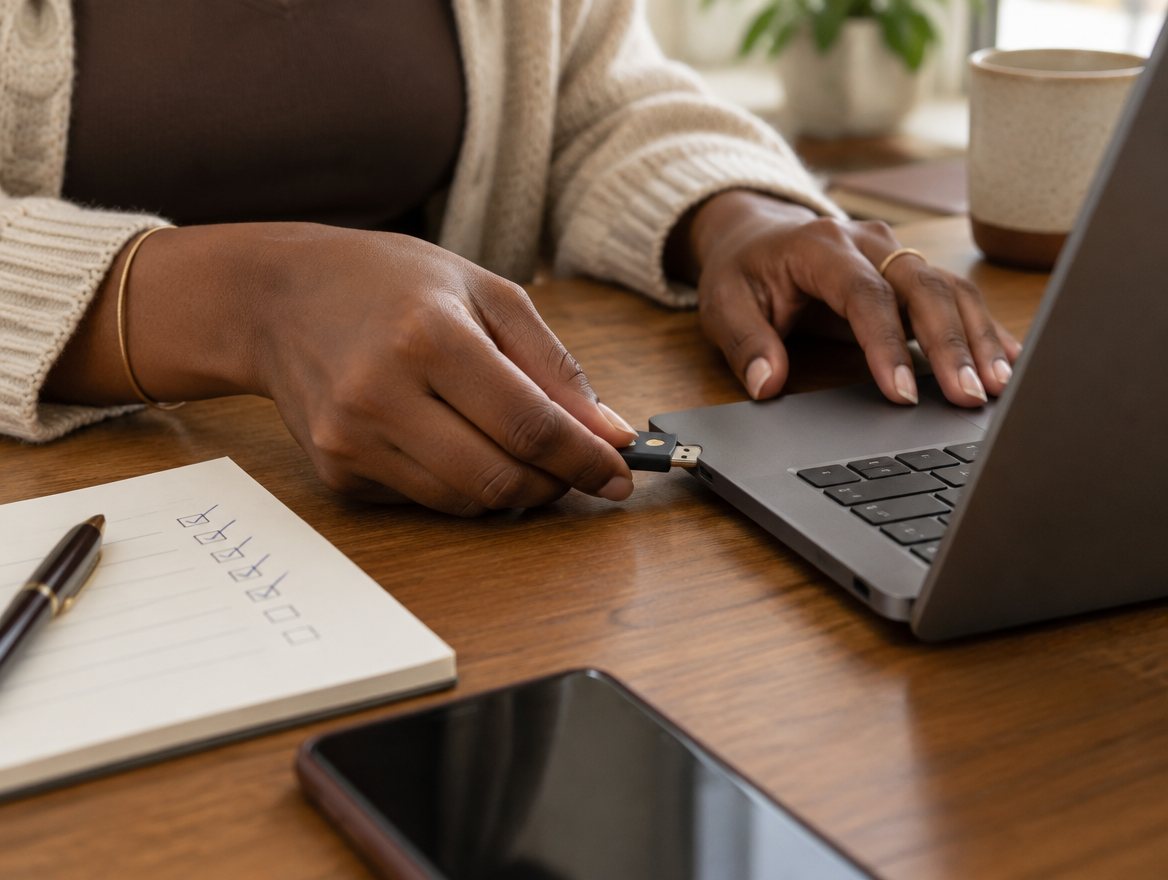
Each admin signs in with a password plus a code from their phone or a security key.
04
We add file and login protection.
Repeated failed logins get blocked, file permissions are locked down and risky server settings are switched off.
05
We set up off-site backups and test a restore.
Copies are kept away from your host. We restore one to a test copy to prove it works.
06
We write up the risks.
A ranked list of what we found, what we changed and what risk remains, in plain words.
BearStackWebsite security
Strengthen your website.
Find the security gaps and agree what to strengthen.
Why BearStack
Security you can check, not just trust
“Secure” isn’t a badge. It’s a list of risks closed, and an honest note of the ones left.
01
We’re honest about what’s left.
No one can make a site impossible to attack. We tell you which risks remain and what would reduce them.
02
Every change is written down.
You, your developer or your insurer can check exactly what we did and why.
03
We test before we hand back.
Sign-in, forms and checkout are checked after the changes, and a backup is restored to prove it works.
04
We assess the problem and confirm the scope and next steps in writing before work starts.
After the initial assessment, you get the price and scope in writing. No hourly meter.
Access
What we need from you
Access lets us start. Here’s what helps, and how to share it without creating a new risk.
Never send passwords by email, text or WhatsApp.We send you a one-time secure link that expires once it’s opened. Already emailed one? Tell us, and we’ll change it first.
Hosting access.A login for your hosting control panel, or SFTP details (a secure way to reach the site’s files).
A separate admin account for us.Create one in your site’s dashboard, and delete it when we’re done.
Who should have access.Staff, agencies and developers you still work with, so we know which logins to keep.
Domain access, only if needed.That’s your registrar, the company you pay for your domain name. We’ll tell you if we need it.
Proof
What you get in writing
A security report you can keep, and share with your developer, host or insurer.
- Risks found, most urgent first
- What changed: accounts, plugins, settings and backups
- What remains, and what would reduce it
- The checks, including the restore test
Security review gives you the ranked risk list only, with no changes made.
Security report
Sample report
Site
yourbusiness.co.uk
Risks found (ranked)
Each risk marked high, medium or low, with what it could lead to
Changed
What we changed, and the risks we left open, with the reason
Checks
- Accounts reviewed and old logins removed
- Updates applied and pages tested
- Two-step sign-in on for every admin
- Off-site backup taken
- Restore test passed
An illustration of the report's format, not a real client.

Let’s talk about your website
Let’s strengthen your website.
Tell us what is worrying you and share your website. We can discuss the accounts, updates and backups that need a closer look.
- 01 Share your website
- 02 Describe the problem
- 03 Agree the next step
FAQ
Questions owners ask us
Not sure which plan you need? Ask during the initial assessment. We'll tell you straight, even if the review alone is enough.
Can you guarantee I won't be hacked?
No. No one can honestly promise that, so be wary of anyone who does. What we can do is close the common ways in, which lowers the risk, and write down the risks that remain, so you can decide what to do about each one.
Will hardening slow my site down?
It shouldn’t. Most of the work is updating software, removing unused code and tightening settings, none of which adds weight. We avoid heavy all-in-one security plugins. We test the main pages after the changes, and if anything is slower, we tell you and adjust it.
Do I need monitoring?
Not always. Hardening holds up best when someone keeps the site updated and checks the backups. If you or your developer already do that, Hardening alone may be enough. If not, monitoring can be agreed after hardening: we keep watching, keep it patched and send a monthly log.
What about my developer?
They’re welcome to stay involved. We share the report with them and agree who updates what, so nothing is done twice. If they still need access, they get their own login with two-step sign-in, not a shared one. We don’t need them to start.
Do you work with sites that aren't WordPress?
Yes. We also harden Joomla, Drupal, custom PHP and plain HTML sites, as long as we can reach the files and the hosting account. On hosted builders such as Wix, Squarespace or Shopify, the platform runs the server, so we focus on your accounts, two-step sign-in, your domain and your email. We confirm the fixed fee during the initial assessment.
How do I share access safely?
We send you a one-time secure link. You paste the login details into it, and it expires once we’ve opened it. Where you can, create a separate admin account for us and delete it when we finish. Never send passwords by email or chat.
What happens if something breaks?
We back up the whole site before we change anything, and test the main pages after each change. If something breaks, we roll that change back, tell you what happened, and agree the fix with you before we try again. It’s all recorded in the report.
How long does it take?
It depends on the size of the site and how much needs changing. We’ll give you a time on the call. We also tell you before any change that affects how you or your staff sign in.
My site was cleaned up recently. Is hardening enough?
If the site is clean, yes: hardening is the right next step. If you still see spam pages, redirects or warnings, it may still be infected. In that case, start with Hacked site cleanup, where the Cleanup and hardening plan covers both.